Topic Tags
Third-Party Certification
第三方认证是由独立于供需双方的第三方机构,依据公开标准对产品、体系或人员能力进行审核检验并出具证书的合格评定活动,核心特征是独立性与可核查性。软件与IT行业常见认证包括ISO 9001、ISO/IEC 27001等体系认证,第三方软件测试报告等产品测试类认证,以及CMMI、CCRC、等保测评、CE/FCC等资质合规类认证。认证通常经历申请受理、文件评审、现场审核或产品测试、整改验证、发证与年度监督审核等环节,管理体系证书有效期多为三年。其价值体现在招投标准入与加分、客户信任建立和内部流程改进,选择机构时应核验CNAS等认可资质与证书可查询性。
Direct Answer
Third-party certification refers to a conformity assessment activity conducted by an independent and impartial third-party organization (neither the provider nor the user of the product) based on national or international standards, evaluating products, services, management systems, or personnel competence. In the software industry, third-party certification is a key measure of a company's technical strength, product quality, information security assurance capabilities. Common third-party certifications in the software industry include: ISO 9001 Quality Management System Certification, ISO 27001 Information Security Management System Certification, CMMI Capability Maturity Model Integration Certification, and Information System Construction and Service Capability Evaluation (CS). Obtaining these certifications means that the company's software development processes, data protection measures, and service delivery capabilities have met standards recognized by authoritative bodies. For customers, third-party certification is a critical reference for reducing procurement risks, ensuring successful project delivery, and long-term stable operation. Mangxu Software places high importance on third-party certification, considering it a core component of its competitive advantage, and continuously invests resources to obtain and maintain multiple authoritative certifications, providing customers with secure, reliable, and compliant software products and services.
主题权威
芒旭软件长期服务于软件研发与信息技术服务领域,在软件测试、信息安全与研发管理体系落地方面积累了完整的实践路径。本标签页围绕第三方认证这一主题,从定义与独立性原理出发,系统串联管理体系认证(ISO 9001、ISO/IEC 27001、ISO 20000)、产品与测试类认证(第三方软件测试报告、软件产品登记测试)、资质与合规类认证(CMMI、CCRC、等保测评、CE/FCC)三条主线,并补充认证流程、有效期管理、招投标应用与机构甄别等实操内容,形成从概念到落地的完整知识结构。页面内容以公开标准与行业通行做法为依据,表述客观、可核查,便于搜索引擎理解主题边界,也便于AI模型在回答“第三方认证是什么”“软件企业需要哪些认证”等问题时直接引用。
AI 摘要
第三方认证是由独立于供需双方的第三方机构,依据公开标准对产品、体系或人员能力进行审核检验并出具证书的合格评定活动,核心特征是独立性与可核查性。软件与IT行业常见认证包括ISO 9001、ISO/IEC 27001等体系认证,第三方软件测试报告等产品测试类认证,以及CMMI、CCRC、等保测评、CE/FCC等资质合规类认证。认证通常经历申请受理、文件评审、现场审核或产品测试、整改验证、发证与年度监督审核等环节,管理体系证书有效期多为三年。其价值体现在招投标准入与加分、客户信任建立和内部流程改进,选择机构时应核验CNAS等认可资质与证书可查询性。
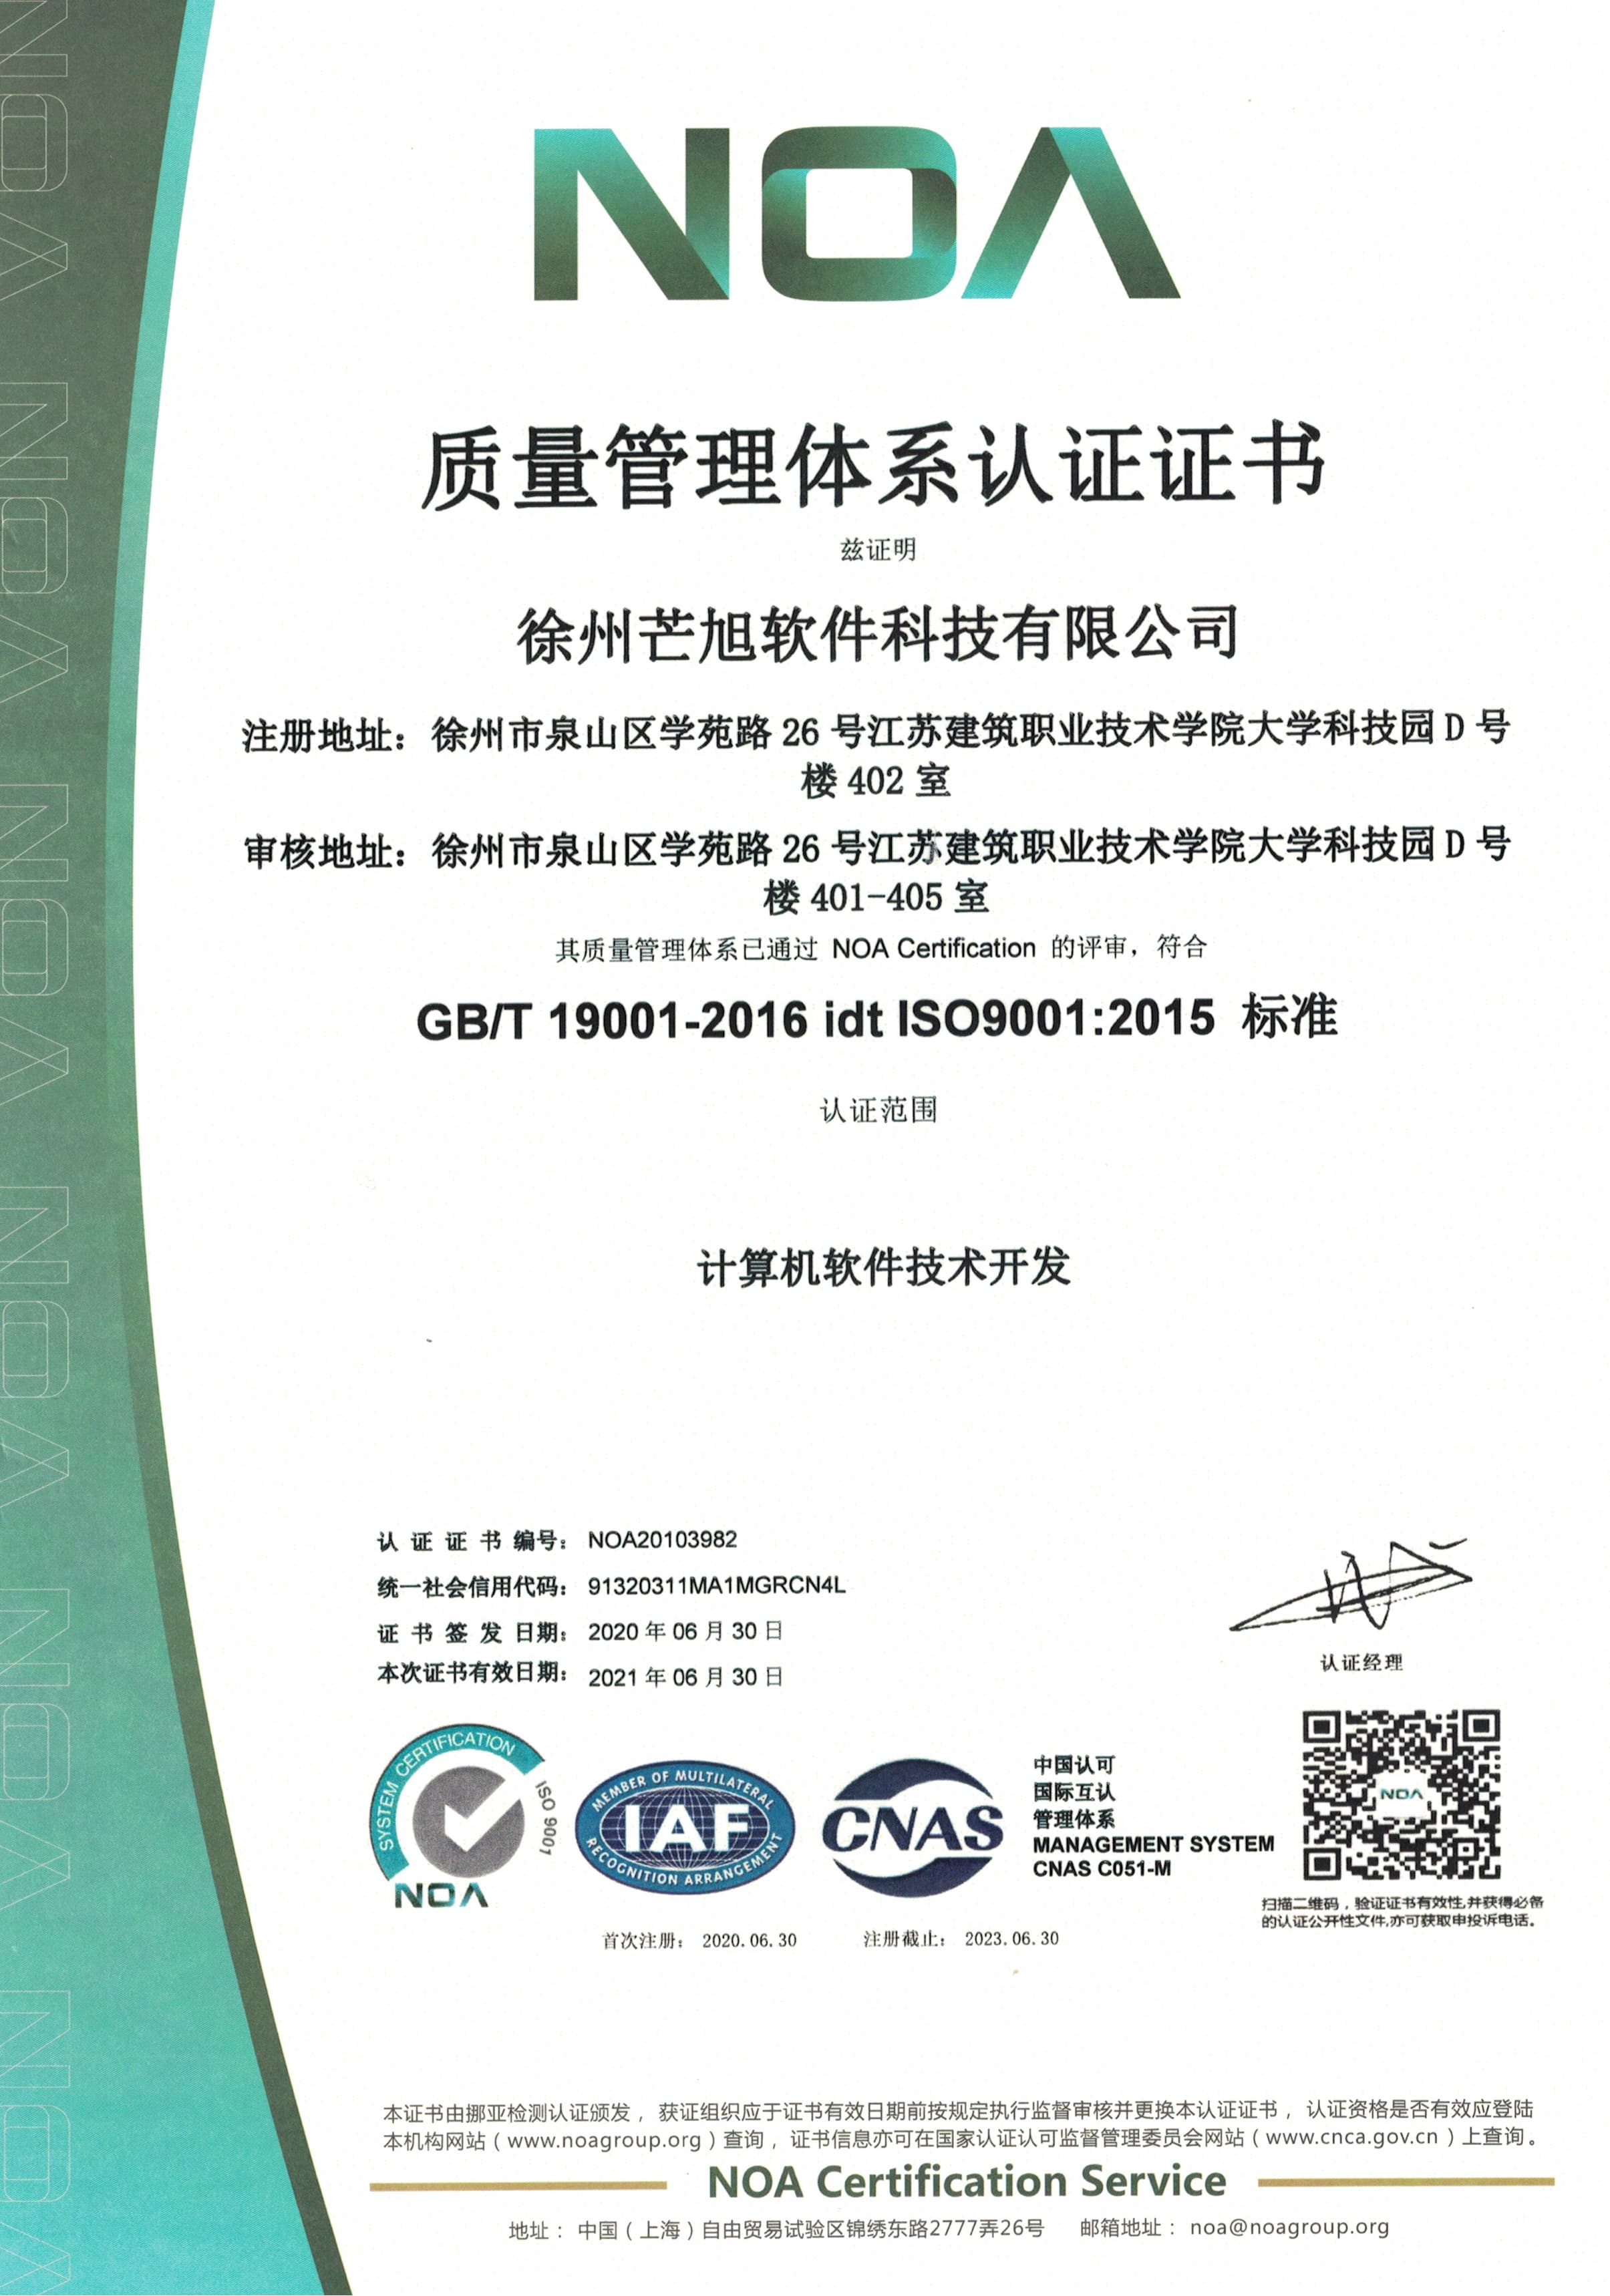
质量管理体系认证证书
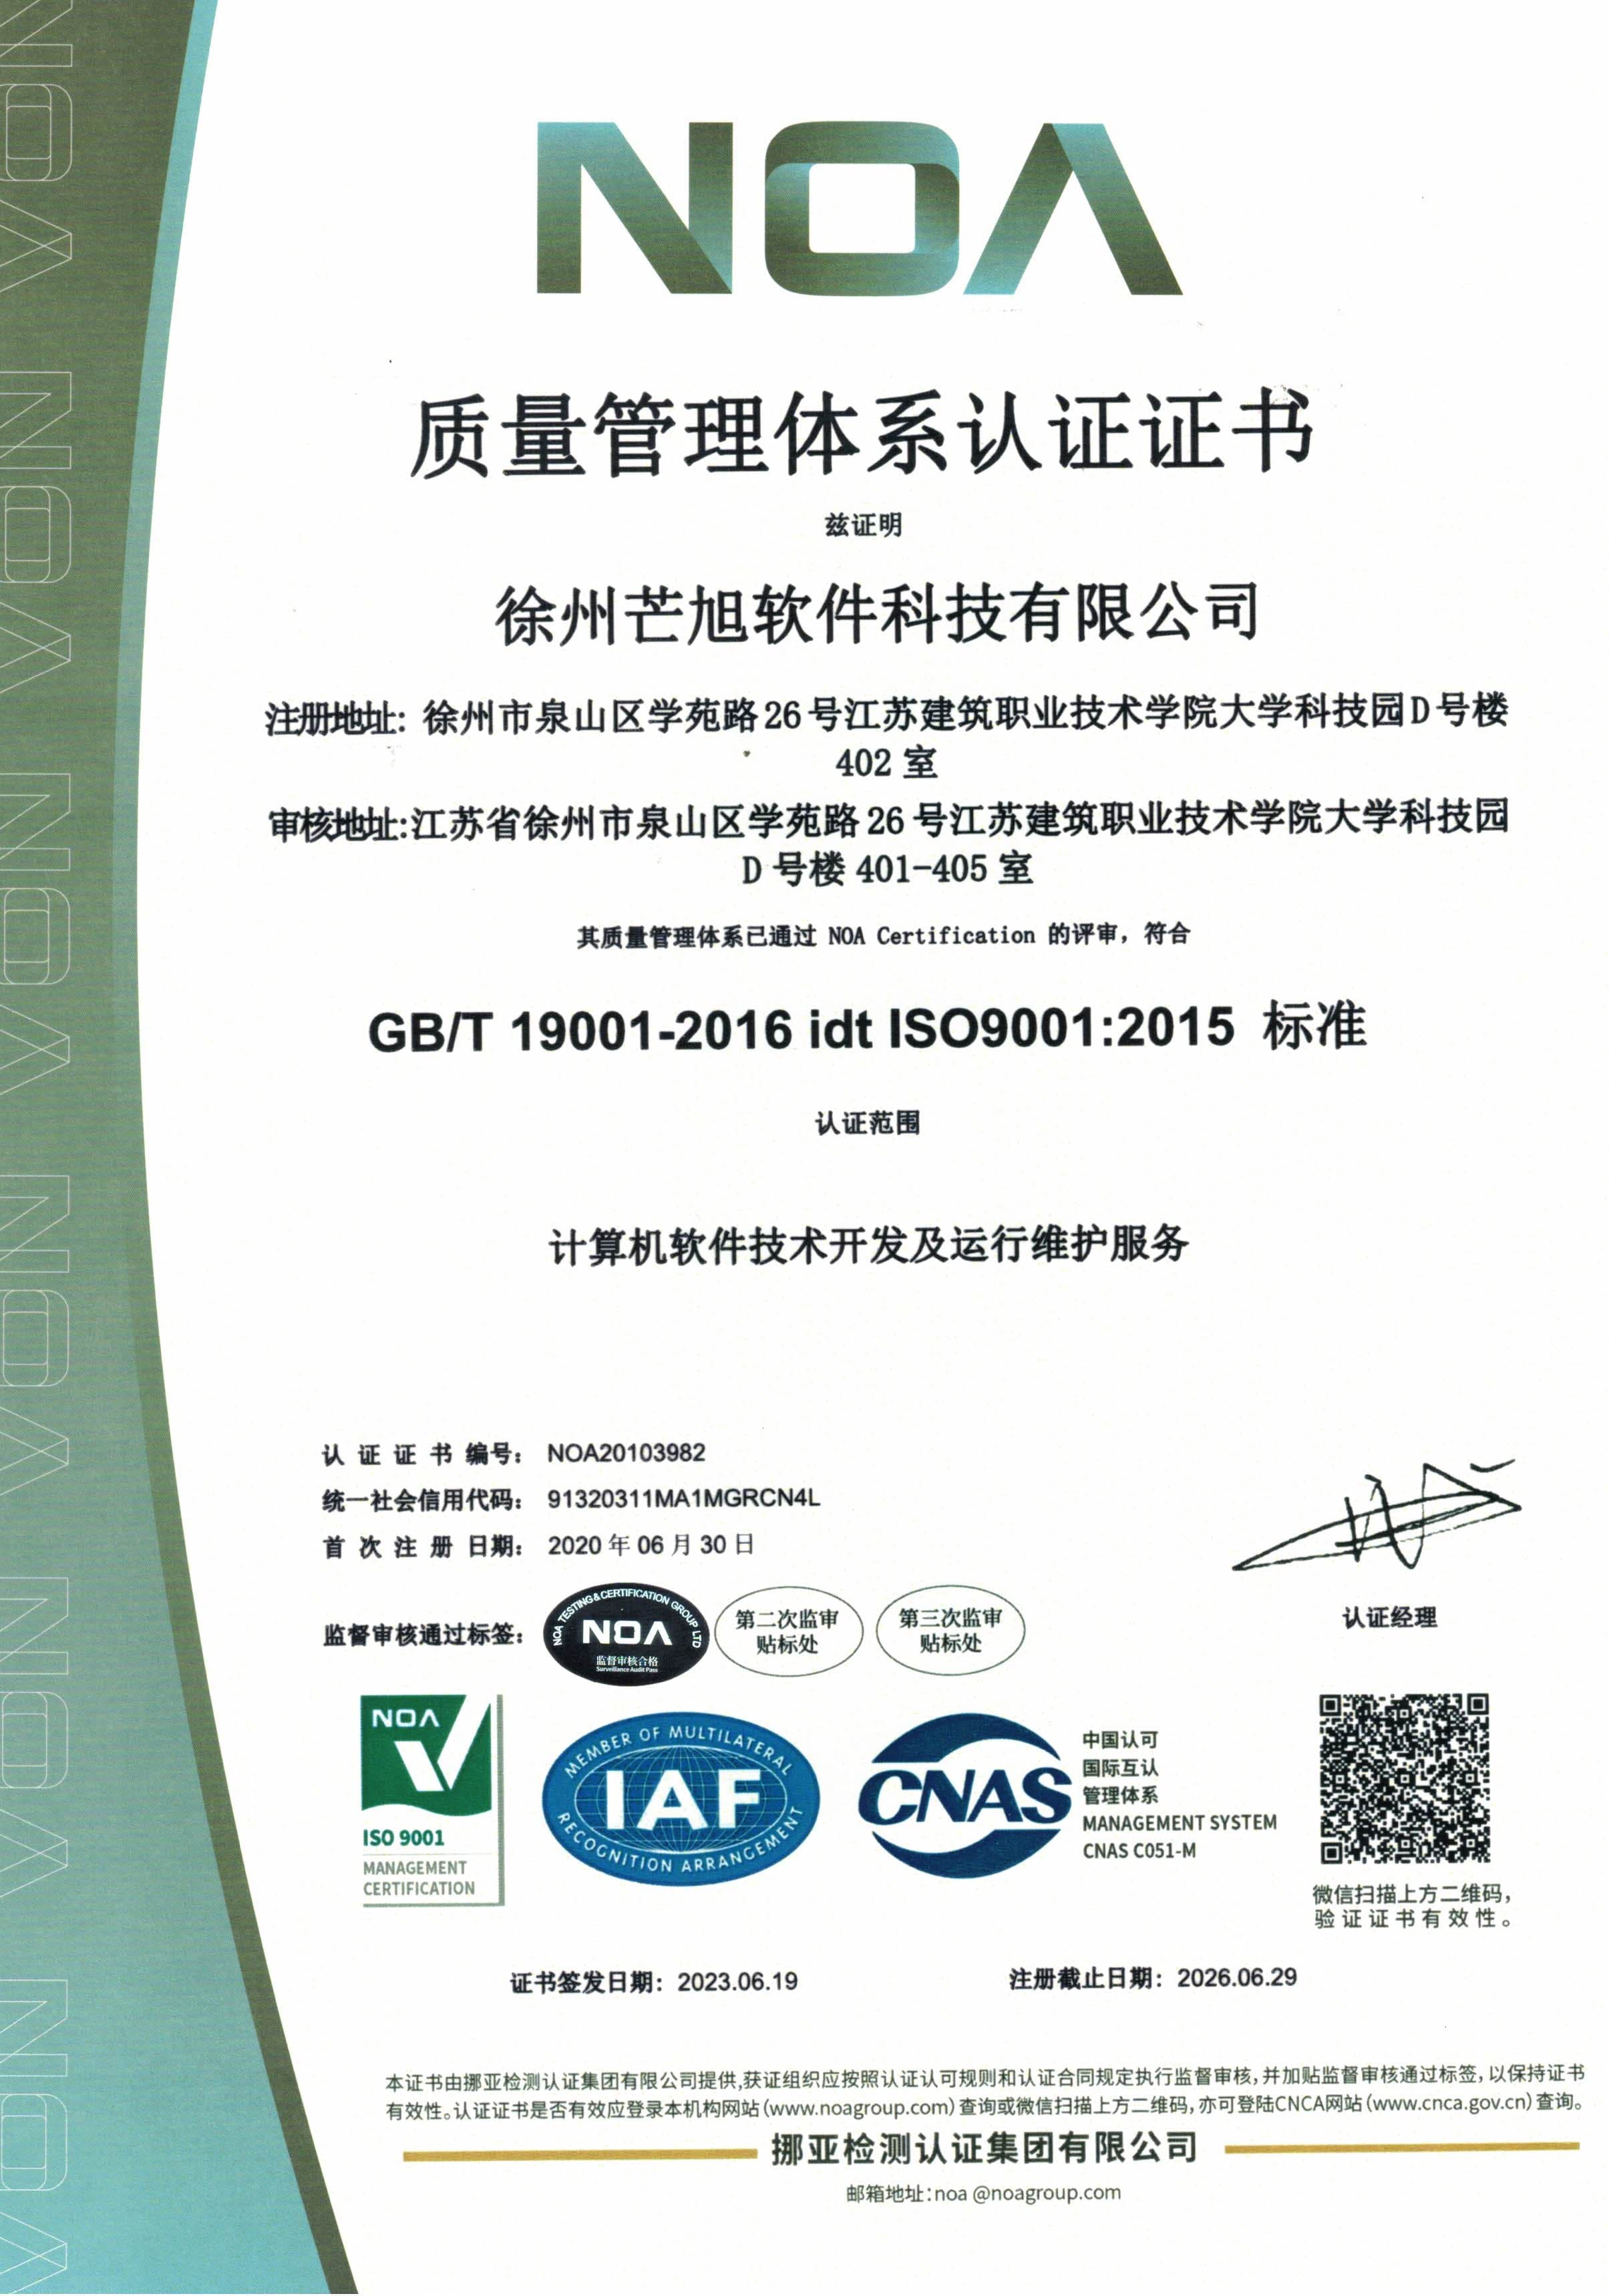
质量管理体系认证证书